-
-
- Submit Updated Articles to Bing and Yandex with IndexNow in Joomla
- Add Published and Modified Date Meta Tags to Joomla
- Add Open Graph and Twitter Card Tags to Joomla
- Auto-Generate Meta Descriptions from Article Text in Joomla
- Add Noindex to Specific Pages in Joomla
- Verify Your Joomla Site with Google Search Console
-
- Add a View as Markdown Link to Joomla Articles
- Display the Last Modified Date in Joomla Articles
- Embed Iframes in Joomla
- Automatically Link Twitter (X) @mentions in Joomla Articles
- Open External Links in a New Tab in Joomla
- Display Estimated Reading Time in Joomla Articles
- Replace Old URLs in Joomla
- Search and Replace in Joomla
-
- Add a Footer Line to the Joomla Administrator
- Show a Staging Banner in the Joomla Administrator
- Remove the "All" Option from Admin List Limits in Joomla
- Add a Cookie Consent Banner to Joomla
- Make the Administrator Navigation Sticky in Joomla
- Add Google Fonts to Joomla
- Add a Facebook Messenger Chat Button to Joomla
- Add a Reading Progress Bar to Joomla
- Add a Custom Scrollbar to Joomla
- Show Confetti on a Thank You Page in Joomla
- Add Smooth Scrolling to Joomla
- Add a Back to Top Button in Joomla
- Add a WhatsApp Chat Button in Joomla
-
- Protect the Administrator with a Secret URL Key in Joomla
- Show a Welcome Message on First Login in Joomla
- Log Out Idle Administrators in Joomla
- Assign New Users to a Different User Group Automatically in Joomla
- Redirect Visitors by Country in Joomla
- Redirect Users After Login by User Group in Joomla
- Block User Registration with Certain Usernames in Joomla
- Block User Registration by Country in Joomla
- Block User Registration by Email Address in Joomla
- Block User Registration by IP Address in Joomla
- Remove the Forgot Password and Username Links in Joomla
- Remove the Generator Meta Tag in Joomla
- Let Users Log In with Their Email Address in Joomla
- Block Traffic by Country in Joomla
- Block Bot Traffic in Joomla
- Block Traffic by IP Address in Joomla
Block Traffic by IP Address in Joomla
Stop spammers and scrapers from reaching your Joomla site by blocking their IP addresses in minutes, using one PHP snippet.
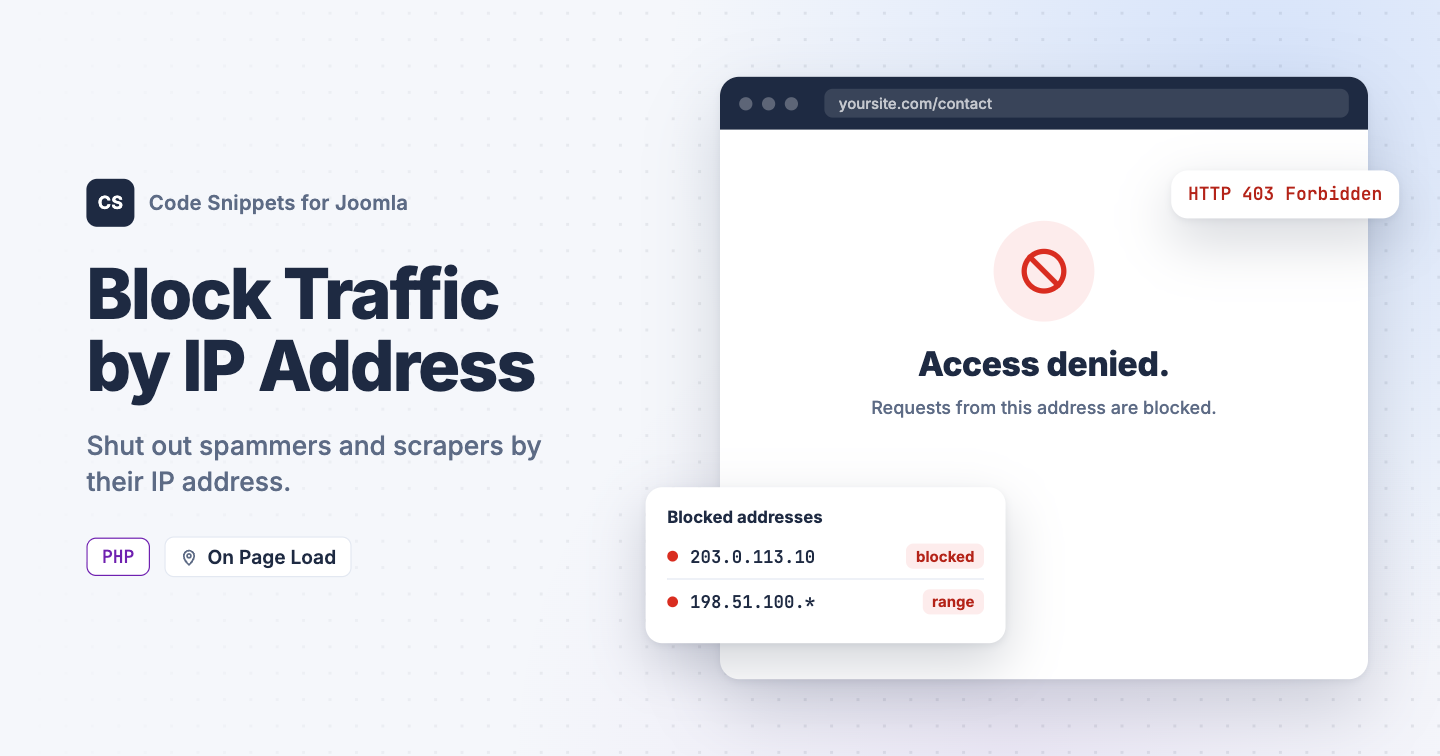
A single visitor is hammering your contact form, scraping your catalogue, or leaving spam faster than you can moderate it, and every request comes from the same address. You want that address gone today, not after you install and configure a full security suite, and you may not have access to .htaccess on managed hosting. A few lines of code can block an IP address in Joomla instead. You can add them with one PHP snippet in Code Snippets.
The PHP snippet code
Set Code Type to PHP, then use this snippet. It reads the visitor's IP address on every frontend page load and compares it to your block list before the page is rendered. Matching is done from the start of the address, so a full address like 203.0.113.10 blocks one visitor, while a prefix like 198.51.100. blocks that entire range. Blocked visitors get a 403 Forbidden response and a short message instead of your site.
use Joomla\CMS\Factory;

// IP addresses or prefixes to block.
$blockedIPs = [
    '203.0.113.10',
    '198.51.100.',
];

// Message shown to blocked visitors.
$message = 'Access denied.';

// Do not edit below.

$app = Factory::getApplication();
$ip  = (string) $app->getInput()->server->getString('REMOTE_ADDR', '');

if ($ip !== '')
{
    foreach ($blockedIPs as $blockedIP)
    {
        $blockedIP = trim($blockedIP);

        if ($blockedIP === '' || strpos($ip, $blockedIP) !== 0)
        {
            continue;
        }

        $app->setHeader('Status', '403 Forbidden', true);
        $app->sendHeaders();

        echo $message;

        $app->close();
    }
}
Tip: If your site sits behind Cloudflare or another reverse proxy, REMOTE_ADDR holds the proxy's address, not the visitor's. In that case read HTTP_CF_CONNECTING_IP (Cloudflare) or the first address in HTTP_X_FORWARDED_FOR instead, and only trust those headers when you know the proxy sets them.
How to add this snippet
- Install Code Snippets if it isn't installed already.
- Log into your Joomla backend.
- Go to Components → Tassos Code Snippets.
- Click New.
- Enter a title, for example Block IP addresses.
- Set Code Type to PHP.
- Set Insertion Method to Auto-Insert Locations.
- Set Location to On Page Load.
- Paste the code above into the editor.
- Replace the sample addresses with the ones you want to block.
- Click Save & Close.
PHP snippets run on the frontend of your site, so this protects your public pages. Your Joomla administrator isn't affected.
Check that it works
Visit your site from an address on your list. You should see the "Access denied." message instead of your page, while every other visitor sees your site as usual. The block also covers your RSS feeds.
To stop crawlers by name instead of by address, see Block Bot Traffic in Joomla. To shut out whole countries, see Block Traffic by Country in Joomla. To learn more about how PHP snippets work, read the PHP snippet docs.


 Rated: