-
-
- Submit Updated Articles to Bing and Yandex with IndexNow in Joomla
- Add Published and Modified Date Meta Tags to Joomla
- Add Open Graph and Twitter Card Tags to Joomla
- Auto-Generate Meta Descriptions from Article Text in Joomla
- Add Noindex to Specific Pages in Joomla
- Verify Your Joomla Site with Google Search Console
-
- Add a View as Markdown Link to Joomla Articles
- Display the Last Modified Date in Joomla Articles
- Embed Iframes in Joomla
- Automatically Link Twitter (X) @mentions in Joomla Articles
- Open External Links in a New Tab in Joomla
- Display Estimated Reading Time in Joomla Articles
- Replace Old URLs in Joomla
- Search and Replace in Joomla
-
- Add a Footer Line to the Joomla Administrator
- Show a Staging Banner in the Joomla Administrator
- Remove the "All" Option from Admin List Limits in Joomla
- Add a Cookie Consent Banner to Joomla
- Make the Administrator Navigation Sticky in Joomla
- Add Google Fonts to Joomla
- Add a Facebook Messenger Chat Button to Joomla
- Add a Reading Progress Bar to Joomla
- Add a Custom Scrollbar to Joomla
- Show Confetti on a Thank You Page in Joomla
- Add Smooth Scrolling to Joomla
- Add a Back to Top Button in Joomla
- Add a WhatsApp Chat Button in Joomla
-
- Protect the Administrator with a Secret URL Key in Joomla
- Show a Welcome Message on First Login in Joomla
- Log Out Idle Administrators in Joomla
- Assign New Users to a Different User Group Automatically in Joomla
- Redirect Visitors by Country in Joomla
- Redirect Users After Login by User Group in Joomla
- Block User Registration with Certain Usernames in Joomla
- Block User Registration by Country in Joomla
- Block User Registration by Email Address in Joomla
- Block User Registration by IP Address in Joomla
- Remove the Forgot Password and Username Links in Joomla
- Remove the Generator Meta Tag in Joomla
- Let Users Log In with Their Email Address in Joomla
- Block Traffic by Country in Joomla
- Block Bot Traffic in Joomla
- Block Traffic by IP Address in Joomla
Protect the Administrator with a Secret URL Key in Joomla
Hide your Joomla login page behind a secret key in the address and log every blocked attempt, so bots and password guessers never see it, using one PHP snippet.
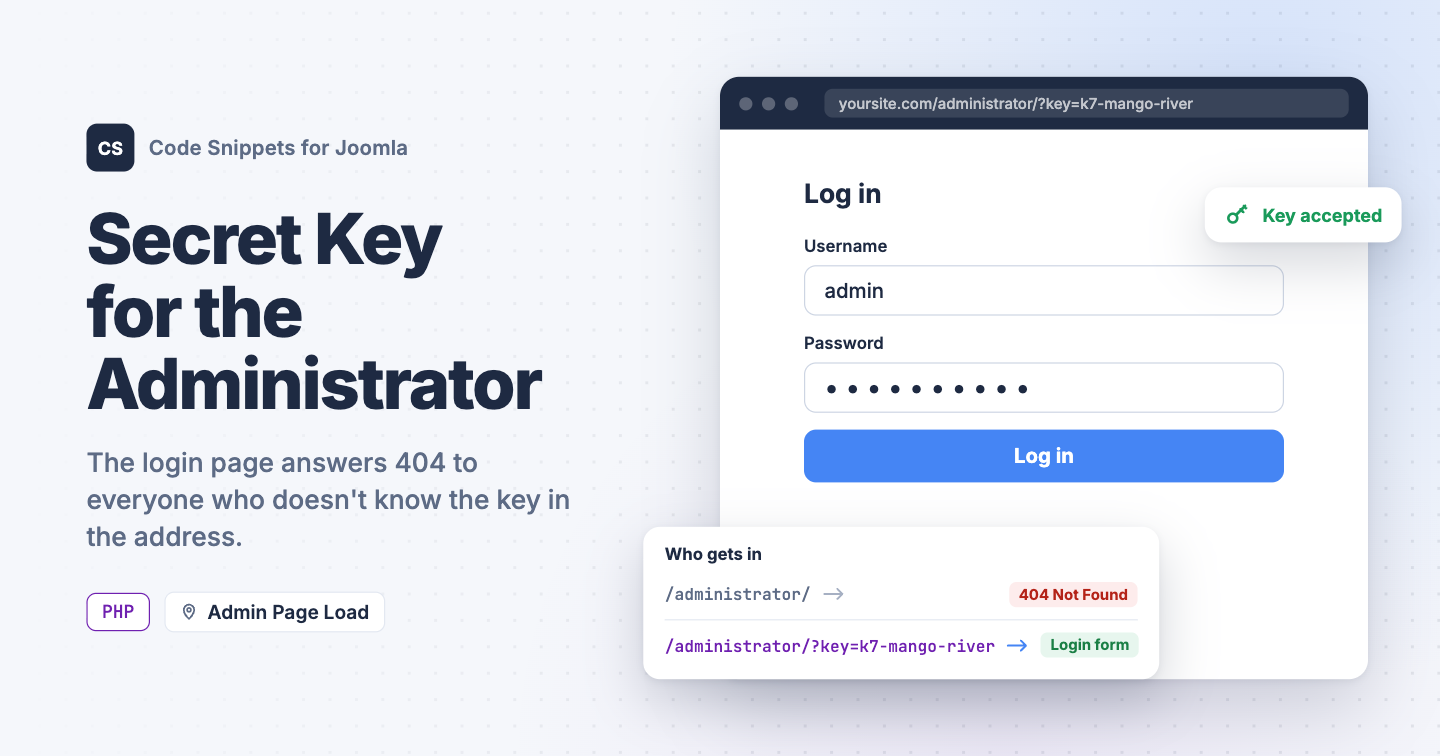
Every Joomla site has its login page at the same address, /administrator, so bots find yours in seconds and hammer it with password guesses all day. A secret key in the address fixes that: the page answers with a 404 to everyone who doesn't know the key, and every blocked attempt lands in a log file. You can add this to the Joomla administrator with one PHP snippet in Code Snippets.
The PHP snippet code
The snippet runs before every administrator page. Logged-in users pass. A browser that opened the administrator with the right key in the last 30 days passes. Everyone else gets a plain 404 answer, with no Joomla session cookie, and the snippet writes the date, address and requested URL to administrator/logs/admin_key.php.
use Joomla\CMS\Factory;
use Joomla\CMS\Log\Log;
use Joomla\CMS\Uri\Uri;

// The secret. Open yoursite.com/administrator/?key=SECRET once per browser.
$key = 'change-me';

// Do not edit below.

$app   = Factory::getApplication();
$input = $app->getInput();

// Logged-in users are already past the gate. The sample key blocks no one.
if ($key === 'change-me' || !empty($app->getIdentity()->id))
{
    return;
}

// The cookie holds a signature of the key, never the key itself.
$cookie = 'tcs_admin_key';
$token  = hash_hmac('sha256', $key, $app->get('secret'));

if (hash_equals($token, $input->cookie->getString($cookie, '')))
{
    return;
}

if (hash_equals($key, $input->get->getString('key', '')))
{
    // The browser keeps access for 30 days.
    $input->cookie->set($cookie, $token, [
        'expires'  => time() + 30 * 86400,
        'path'     => Uri::base(true),
        'secure'   => $app->isHttpsForced(),
        'httponly' => true,
    ]);

    // Reload the page without the key, so it stays out of the address bar.
    $uri = Uri::getInstance();
    $uri->delVar('key');
    $app->redirect($uri->toString());
}

// Log the attempt in administrator/logs/admin_key.php, then answer with a 404.
$logger = [
    'text_file'         => 'admin_key.php',
    'text_entry_format' => "{DATETIME}\t{CLIENTIP}\t{MESSAGE}",
];
Log::addLogger($logger, Log::INFO, ['adminkey']);
Log::add(Uri::getInstance()->toString(['path', 'query']), Log::INFO, 'adminkey');

header_remove('Set-Cookie');
http_response_code(404);
die('404 Not Found');
Replace change-me in $key with your own key, and keep it long. The snippet does nothing while the key still reads change-me, so pasting it as it is can't lock you out.
A browser keeps access for 30 days after one visit with the key. The cookie holds a signature of the key, never the key itself, so changing $key locks every browser out again until it visits with the new one.
How to add this snippet
- Install Code Snippets if it isn't installed already.
- Log into your Joomla backend.
- Go to Components → Tassos Code Snippets.
- Click New.
- Enter a title, for example Administrator secret key.
- Set Code Type to PHP.
- Set Insertion Method to Auto-Insert Locations.
- Set Location to Admin Page Load (Pro).
- Paste the code above into the editor.
- Replace
change-mewith your own key, for examplek7-mango-river. - Leave Access set to Public. The visitor who opens the login page isn't logged in yet, and the snippet only runs for that visitor when it's public.
- Click Save & Close.
Your current browser is logged in, so nothing changes for it. Every other browser now needs the key once: https://yoursite.com/administrator/?key=k7-mango-river. The key works on any administrator address, so a link to a specific screen with &key= added opens that screen.
Check that it works
- Open a private browser window and go to
https://yoursite.com/administrator/. - In the same window, go to
https://yoursite.com/administrator/?key=followed by your key. - Open
administrator/logs/admin_key.phpon your server with FTP or your host's file manager.
The first address shows a plain "404 Not Found" message. The second shows the Joomla login page, and the key disappears from the address bar. The log file holds one line for the first visit, with the date, the address it came from and the URL it asked for.
public $tcs_safe_mode = true; to configuration.php. It pauses every snippet, so you can log in, fix the key, and remove the line again. Links to the administrator in Joomla's emails, like the update notice, open a 404 in a browser that has never visited with the key. Open the administrator with the key first, then follow the link.
To keep known troublemakers off the whole site, see Block Traffic by IP Address in Joomla, and to close sessions left open on shared computers, see Log Out Idle Administrators in Joomla. To learn more about how PHP snippets work, read the PHP snippet docs.


 Rated: